I put a real login in front of a Lovable app with Cloudflare Access and Auth0.
An app you generate with AI is open to anyone who has the link. In a September 2025 video I showed how I put a real login screen in front of one with Cloudflare and Auth0, without writing a line of app code.
The business case
AI app builders get you a working app in minutes. They don't decide who gets to use it. If the app touches your business or your team's work, an open URL is a problem.
The setup I showed was free for up to 50 users. Cloudflare Zero Trust sits in front of the app and asks for a login before anyone reaches it, and Auth0 handles the accounts. The end state in the video was a login page with your logo, email and password fields, and a sign-up button. I called it production-grade security for free, with no code written.
Security is a big topic, and I said up front that one video can't cover all of it. What it gives you are the pieces to lock down any vibe-coded app. For the code side of the same problem, see why vibe coding still needs engineering judgment. This setup fits an internal or team app best. I said it can handle sign-ups, but it isn't the best workflow for that.
Get the app onto Cloudflare
My demo was an AI teleprompter called Talk Topic that I generated in Lovable. Any AI app generator works. You need three accounts: GitHub, Cloudflare and Auth0.
Lovable's built-in GitHub connection moved the code into a new repo. In Cloudflare I went to Compute, then Workers & Pages, created a Cloudflare Worker and imported that repo. The first deploy failed, and I expected it to. Lovable's output doesn't carry the settings Cloudflare needs.
I cloned the repo with the GitHub CLI, opened it in Visual Studio Code and asked GitHub Copilot to add the Cloudflare Workers configuration. I pasted the build errors in as context. In about 5 minutes it added a Wrangler config file, which tells the build where the static HTML, CSS and JavaScript bundle lives.
A second deploy failed on a missing directory. I pasted that log back into Copilot, committed the fix, and the build went through. From then on, every push to the repo triggered a new Cloudflare build and publish.
Public until you lock it
Once it deployed, the app lived on a Cloudflare worker URL, and anyone could open it. As I put it in the video, I was technically no further along than I was with Lovable.
The next step is registering the app in Auth0. I'm not affiliated with them, but I've used them for years, and they're owned by Okta. I created an application and picked Regular Web App, even though the app itself is a single-page app. Then I collected three values from its settings: the domain, the client ID and the client secret.
Jump to
- 0:00 Introduction
- 1:07 Overview of Vibe Coded App
- 1:54 Connecting GitHub and CloudFlare
- 3:10 Configuring CloudFlare for Deployment
- 4:07 Fixing Deployment Issues
- 6:21 Using Visual Studio Code for Configuration
- 9:12 Deploying and Testing the Application
- 9:44 Introduction to Auth0 and Okta
- 11:23 Setting Up Zero Trust with CloudFlare
- 14:54 Setting Up CloudFlare Authentication
- 15:27 Configuring DNS and CloudFlare Worker
- 16:29 Integrating Auth0 with CloudFlare
- 18:10 Obtaining Configuration URLs via ChatGPT
- 19:35 Finalizing Auth0 Setup
- 20:48 Testing and Troubleshooting
- 24:23 Creating and Applying Security Policies
- 27:55 Conclusion and Next Steps
I walk through every click on screen in the full video on my channel: securing a vibe-coded app with Cloudflare on YouTube.
Put Access in front
In Cloudflare Zero Trust you first name your team, which stands for your organization. Remember that name. It comes back later in the login URLs.
On the free plan, up to 50 users could use the app before paid seats kicked in. It still asked me for a payment method. In the video I said you'd pay $7 per user once you passed 50. As of October 2026, Cloudflare's plans page lists a free tier for up to 50 users and Pay-as-you-go at $7 per user a month, and that plan bills every user, not just the ones past 50. Check it before you count on those numbers.
Go to Access, then Applications, and add a self-hosted application. Session duration is how long before someone has to log in again. I suggested 15 minutes for something sensitive and 30 minutes to 6 hours otherwise. Set the public endpoint to the worker's domain. To use your own domain, add it as a custom domain under the worker's Domains & Routes settings and point your registrar at Cloudflare. After I saved, a refresh of the app showed Cloudflare's block page. Cloudflare has renamed these menus since September 2025. As of October 2026, its self-hosted app guide has you go to Access controls, then Applications, and add a public hostname, which has to be a domain on your Cloudflare account. Login methods now sit under Integrations, then Identity providers.
Connect Auth0 with OpenID Connect
Under login methods, add a new one and choose OpenID Connect. Skip the Okta option, even though Okta owns Auth0. Paste in the Auth0 client ID and client secret.
The next part got wonky. Cloudflare wants an authorization URL, a token URL and a certificate URL, and the Auth0 dashboard doesn't show them. I asked an AI chat assistant for Auth0's well-known configuration URL, opened it in the browser, and copied the authorization endpoint, the token endpoint and the JWKS URL. Auth0 documents that discovery endpoint, and Cloudflare's generic OIDC guide lists the same fields. I also turned on PKCE for extra security.
Back on the Access application, select only the new login method and turn on instant auth, which skips the identity provider picker.
The first login attempt errored, which I expected. Auth0 didn't know about Cloudflare yet. The error details include a callback URL built from your Zero Trust team name. Paste it into Auth0's Allowed Callback URLs. Then paste the base of that URL, with the path removed, into Allowed Logout URLs and Allowed Origins.
The error that cost me a night
Next came "This account does not have access." It kept coming back. I got so frustrated that I shut my computer at about 4 AM and went to bed. When I came back hours later, it worked. My read is that Cloudflare and Auth0 take a while to sync.
If you hit it, re-check every field on the login method: the app ID, the client secret and each URL. Then click Test. If the test passes, you haven't done anything wrong.
Tighten it with policies
A policy is a rule. I made one called North America only and allowed Canada and the United States. You can add rules for specific email addresses, or require two-factor, SMS or one-time password checks. Creating a policy doesn't apply it. Attach it to the application, confirm, then save the application.
To test logging out, use a fresh incognito window. An existing Cloudflare session lets you straight back in.
What the login is for
The point is to get the app you built in front of the people who need it, and nobody else. I said in the video that a deeper breakdown of the moving parts was coming. If you want to understand how Cloudflare fits together from the ground up, start with my free Cloudflare course.
About Dwain
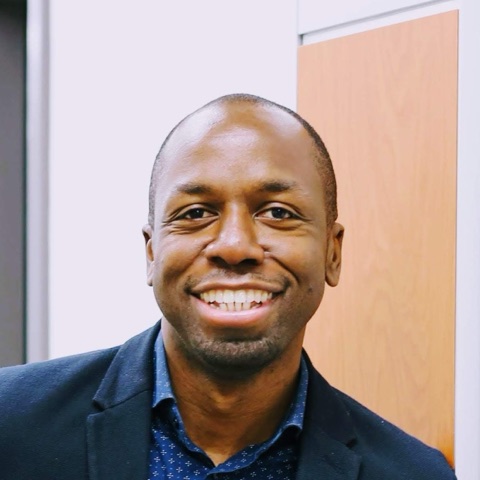
I'm Dwain Browne, Founder of LeadScore AI and SnapSuite. I'm a Toronto-based software architect with 25+ years across software, sales, operations and entrepreneurship. SnapSuite helps contractors and trades teams get paid faster, and LeadScore AI shows you which leads deserve your next call. I also run Vibe Code to Profit, a community helping people build software with AI.